
Corporate Conference Security, Protecting Business Events
A corporate conference concentrates, in one venue and over a few hours, everything an organisation usually keeps separated, which is why corporate conference security deserves deliberate planning. The leadership team, the investors, the product roadmap, the financial figures and the key people who hold them. That concentration is exactly what makes business events attractive to opportunists, activists, industrial competitors and, increasingly, to actors who never set foot in the building.
Corporate conference security is therefore not a question of placing a few officers at a door. It is a structured discipline that protects people, access, information and operational continuity. This guide explains how that discipline is built, from the first threat assessment to the post event debrief.

Corporate Conference Security, Protecting Business Events
Reading time: ~13 min
What Corporate Conference Security Actually Covers
Scope of corporate conference security
Corporate conference security is the coordinated protection of attendees, executives, speakers, venues, equipment, sensitive information and corporate reputation against physical, operational and cyber threats. A serious security programme covers venue safety, personal protection, access management, information handling, event continuity, emergency response, transport and parking, and the digital systems used during the event.
At IPS BODYGUARD, we approach business conference security as a management function rather than a staffing exercise. We design the security concept, run the risk assessment, define the protective measures and manage their delivery through a network of licensed local partners in more than 100 countries. The organiser keeps one accountable point of contact, whether the conference takes place in Paris, on the French Riviera, in London, Dubai or Singapore.
The Dual Exposure, People And Information
People and information as joint assets
Most conference security plans concentrate on bodies in a room. That is only half the exposure. A leadership summit, an annual general meeting or an investor conference is also a rare physical gathering of confidential information. Draft results are discussed in corridors. Merger scenarios appear on slides. Phones, laptops and presentation remotes connect to networks nobody audited.
Guidance issued by the United States Department of Defense for classified conferences insists on the same principles for sensitive meetings, verification of participants, badge control, protection of documents, inspection of the rooms used and, where justified, technical countermeasures against unauthorised audio or visual capture.
The need to know principle applies to corporate events as much as to government ones. Not every attendee needs access to every session. Not every vendor needs access to the room where the board rehearses. Zoning the venue by sensitivity, and enforcing that zoning with credentialing, is one of the highest value measures available to an organiser.
The Main Security Risks At Business Conferences
Recurring corporate conference threat families
A site specific risk assessment will always produce a sharper picture than a generic list, but the recurring risk families are well documented across institutional guidance such as the USDA Conference and Training Security Assessment Guide.
Unauthorised access, with intruders exploiting unmanned side doors, loading bays, service corridors or badge sharing during breaks.
Targeted threats against executives and keynote speakers, including hostile approaches at arrival and departure points.
Disruption and crowd incidents, from a single hostile individual interrupting a session to an organised protest at the entrance.
Medical emergencies, which must be anticipated at any large gathering, with defined first aid points and evacuation routes.
Information compromise, through eavesdropping, photography of screens, unattended documents, lost devices or social engineering of staff.
Cyber incidents affecting registration platforms, event applications, presentation systems, voting tools and conference Wi Fi.
Good to know
The United Kingdom National Cyber Security Centre publishes dedicated guidance for high profile conferences, built around governance, risk assessment, incident management and exercising. Its core message is that cyber preparation belongs inside the general event plan, not in a separate technical silo.
What A Conference Security Plan Includes
Core components of a conference security plan
A credible conference security plan is a written document, not a verbal arrangement. It begins with a threat assessment covering the attendee profile, the public visibility of the speakers, the political or social context around the company, the venue layout and the surrounding area. It then defines the protective architecture, perimeter security, entry points, screening procedures, zoning, CCTV surveillance coverage, security staffing levels and shift patterns.
The plan must also define behaviour. Who escalates an incident and to whom. What the emergency communication protocol is when radios fail. Which exits are used for an evacuation and who sweeps which floor. How VIP arrival and departure coordination works when three principals land within the same twenty minutes. Where the medical point sits and which hospital is on standby. Risk management frameworks such as ISO 31000 provide a useful backbone for documenting this logic in an auditable way, which matters when a corporate security director or a family office manager has to justify the arrangement to a board.
The final section of the plan is the one most often skipped, the post event security debrief. Badge recovery, sweep of technical and VIP areas, incident log consolidation, lessons learned and an updated baseline for the next edition.
Access Control And Credentialing
Practical access control measures
Access control is the backbone of corporate meeting security. Institutional guidance recommends identifying and securing every entrance, exit and critical door before the event opens, and maintaining a clear distinction between attendees, staff, contractors, media and security personnel. In practice, conference access control relies on a verified guest list, printed or digital badges with distinct visual categories, identity verification at first entry, controlled readmission after breaks, and supervised access to executive lounges and backstage areas.

Last minute accreditation is where most systems fail. A single registration desk authorised to issue badges, a named approver for exceptions and a written log of every late credential will prevent the vast majority of access incidents. Badge verification should be visible and consistent, including for people everyone recognises, because inconsistent enforcement is what makes an exception possible.
Executive Protection For Corporate Events
A chief executive on stage is a predictable, publicised, stationary target in a known location at a known time. That is why executive protection for corporate events is planned separately from general event security. The protective detail works on the margins of the programme, the vehicle approach, the private entrance, the holding room, the route to the stage, the signing or networking sequence and the departure.
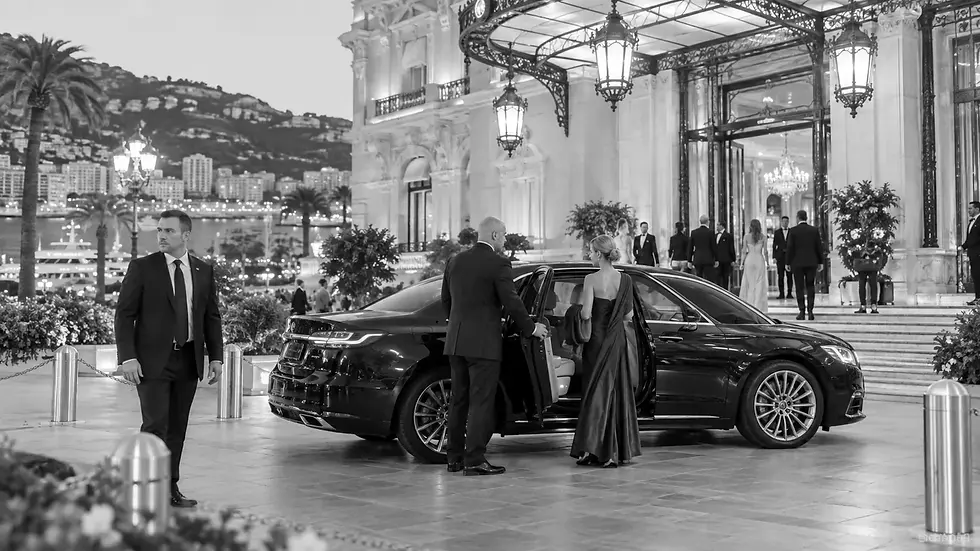
Close protection at a conference is deliberately low profile. Plainclothes agents blend into the business audience, while uniformed security officers hold the visible perimeter. Counter surveillance observes who is observing, a discipline that matters when activist groups or hostile media document arrival patterns. Secure transportation and security drivers close the loop between the airport, the hotel and the venue, and our secure transportation planning is detailed on our dedicated page.
For principals attending several events across different countries in the same season, continuity is the real differentiator. The same security management, the same briefing standard and the same reporting format in Paris, Monaco, Geneva or Dubai removes the fragmentation that corporate security directors are usually asked to eliminate.
Crowd Management And Emergency Response
Conference crowd management services deal with flows rather than crowds in the stadium sense. Arrival peaks at registration, coffee break congestion, plenary room capacity, lift bottlenecks and simultaneous session changes. Each of these creates friction points where an incident becomes harder to detect and harder to resolve.
The conference emergency response plan should cover fire, bomb threat, suspicious package, intrusion, crowd surge, assault, medical emergency, severe weather, power failure, cyber incident and the specific scenario of extracting a principal from a hostile situation. A mobile response team held in reserve, with no fixed post, gives the event manager the flexibility to deal with the unplanned. Every scenario should be briefed to the venue staff, the audiovisual team and the organiser, not only to the security team, because the first person to notice an anomaly is rarely wearing a radio.
Cybersecurity And Intellectual Property Protection
Intellectual property protection at corporate events starts with physical discipline. Screens positioned away from windows and corridors. Printed documents numbered and collected. Photography policy announced and enforced in sensitive sessions. Rooms checked before confidential discussions. Devices never left unattended in meeting rooms.

It continues with digital hygiene. Segmented Wi Fi for speakers and delegates, controlled use of USB media, vetted audiovisual suppliers, disabled default credentials on conference equipment and a tested incident management procedure. Threat intelligence monitoring before and during the event adds an early warning layer, tracking public calls to disrupt, doxxing activity against executives and chatter around the venue. Our approach to digital exposure and awareness covers this layer in more detail.
Important
Sensitive information handling is a people problem before it is a technology problem. A short pre event security briefing for speakers, assistants and hosts usually reduces more risk than any additional piece of hardware.
How Many Security Officers Does A Business Conference Need
There is no reliable ratio of officers per guest. The correct number is derived from the venue, not from the headcount. It depends on the number of entrances to be held, the hours of operation, the screening level, the number of restricted zones, the presence of protected principals, the threat assessment and the local regulatory framework. A compact conference of two hundred people in a resort with multiple open accesses can require more security staffing than a thousand delegates in a single controlled auditorium.
Any provider quoting a staffing figure before conducting a venue security audit is pricing a guess. A proper proposal states the posts, the shifts, the supervision structure, the relief arrangements and the escalation matrix.
Armed Or Unarmed, A Risk Based Decision
The question of armed security at corporate conferences must be answered by local law first, then by the assessed threat, the venue policy, the attendee profile and the recommendations of qualified professionals and law enforcement. In most European jurisdictions, including France, firearms are tightly restricted in private security and the default posture for a business conference is unarmed, discreet and procedurally strong. The decision should always be risk based rather than reflexive, and documented in the security plan.
How To Choose A Conference Security Company
Selecting a conference security company is a due diligence exercise. The following criteria consistently separate a structured partner from a simple supplier of bodies.
Criterion | What to look for |
Relevant experience | Corporate conferences, annual general meetings, investor events, product launches and international venues |
Documented methodology | A written risk assessment, a security plan, a responsibility matrix and an escalation procedure |
Verified compliance | Locally licensed partners, trained and vetted personnel, close protection credentials and professional liability insurance, in line with standards promoted by bodies such as ASIS International and, in the United Kingdom, the Security Industry Authority |
Coordination capability | Ability to work with the venue, the audiovisual team, medical services, transport providers, the IT department and local authorities |
Multilingual reach | International capability so the same standard applies across the full event calendar |
Transparent reporting | Incident logs and a structured post event debrief |
You can review our approach to protective operations and request a tailored assessment through our quotation page.
Building A Security Programme That Holds
A business conference is a controlled environment only if someone has taken the time to control it. The organisations that run events without incident are rarely the ones with the most visible security, they are the ones that assessed the risk early, designed the access architecture properly, protected their executives discreetly and treated their information with the same seriousness as their people. That is the standard we apply when we design and manage conference security programmes, from a single board meeting on the French Riviera to a multi city executive roadshow.
FAQ
How far in advance should conference security planning start?
Ideally before the venue is contractually confirmed, because the site survey can influence the choice of location. When that is not possible, four to six weeks allows time for the risk assessment, the staffing structure, the liaison with the venue and a briefing cycle. The more notice, the better the result. Short notice mobilisation remains possible within 24 to 72 hours minimum, once the contract is signed and payment received, but it reduces the margin for advance work.
Can security be arranged for a hybrid or livestreamed conference?
Yes, and it should be. A streamed event extends the audience far beyond the room, which changes the exposure of speakers and the sensitivity of what appears on screen. The plan then includes broadcast delay considerations, control of what cameras capture and management of the online dimension.
Who holds authority during an incident, the organiser or the security team?
The security plan must state this before the event. In practice, the security manager takes operational decisions on safety matters, the organiser decides on programme matters such as suspending or resuming a session, and both work from a shared escalation matrix agreed in advance.
Is security necessary for a small executive meeting?
Sometimes more than for a large one. A closed meeting of ten decision makers can carry a far higher information value than a conference of a thousand delegates. Measures are simply different, discreet protection, room checks, controlled documentation and secure transport rather than visible officers.
What should be done after the conference ends?
Secure the departure of principals, sweep technical and executive areas, recover badges and sensitive material, consolidate the incident log and run a structured debrief. The output becomes the baseline for the next edition and shortens the planning cycle significantly.


Comments